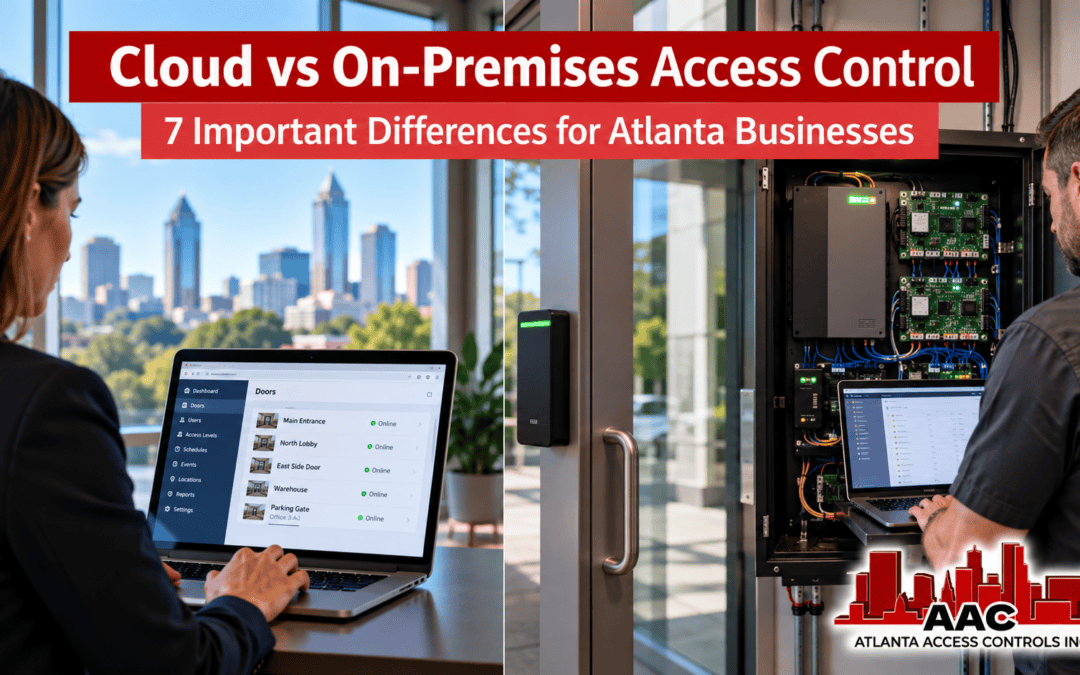
Cloud vs On-Premises Access Control is not simply a choice between newer and older technology. For Atlanta businesses evaluating a commercial access control system, the more important question is how each approach fits the way the organization operates, manages security, plans for growth, and pays for technology over time.
A cloud-managed platform may be attractive to an organization that wants centralized administration, easier management across multiple locations, and an architecture designed to accommodate future expansion. An on-premises system may be the better fit for an organization that wants greater local control, has established IT resources, or prefers a capital investment that avoids depending on continuing subscription expenses.
Neither approach is universally better. One can, however, be clearly better suited to a particular organization once its operational requirements, financial structure, IT resources, security policies, and future plans are understood.
Atlanta Access Controls works with businesses and organizations throughout Metro Atlanta and North-Central Georgia to evaluate commercial access control requirements and determine which system architecture fits those requirements. This guide examines seven important differences between cloud-managed and on-premises access control and explains why those differences matter when planning a system.
Table of Contents
- What Does Cloud vs On-Premises Access Control Actually Mean?
- Difference 1: System Management and Administration
- Difference 2: Remote Access and Multi-Location Management
- Difference 3: Capital Investment vs Recurring Subscription Costs
- Difference 4: IT Infrastructure, Updates and Maintenance
- Difference 5: Cybersecurity Responsibilities
- Difference 6: Scalability and Expansion
- Difference 7: Long-Term Operational and Financial Fit
- When On-Premises Access Control May Be the Better Fit
- When Cloud Access Control May Be the Better Fit
- Questions to Ask Before Choosing an Architecture
- Planning Your Access Control System With Atlanta Access Controls
What Does Cloud vs On-Premises Access Control Actually Mean?
The basic difference involves where important management functions and system resources reside and how authorized administrators interact with them.
In a cloud-managed access control environment, supported management functions are provided through infrastructure and services associated with the cloud platform. Authorized users typically interact with the system through a web-based or application-based management interface, depending on the manufacturer and platform.
The physical security equipment at the facility does not disappear. Doors still require appropriate readers, controllers or intelligent devices, locking hardware, request-to-exit equipment, door-position monitoring, power, and other components required by the system design. The cloud primarily changes aspects of how the system is administered, connected, supported, and expanded.
An on-premises access control system places more of the management infrastructure under the organization’s direct control at the facility or within its own network environment. Depending on the platform, this may include locally hosted software, databases, servers, workstations, controllers, or other system resources.
That distinction does not make one architecture inherently more secure, reliable, or capable than the other. Products vary considerably, and large enterprise on-premises systems can support extensive deployments just as sophisticated cloud platforms can support large multi-location organizations.
The better comparison begins with the business rather than the technology.
Who will administer the system? How many locations must be managed? What internal IT resources are available? How does the organization budget for technology? How quickly might the system need to grow? What cybersecurity policies must be followed? Those questions can have more influence on the right architecture than whether a product is labeled cloud or on-premises.
Businesses that want a broader foundation before comparing these architectures can review Atlanta Access Controls’ Access Control Systems Atlanta guide, which covers commercial access control planning, credentials, system integration, gates, installation, costs, and long-term system considerations.
Difference 1: System Management and Administration
One of the first practical differences between cloud and on-premises access control is how administrators interact with the system during normal business operations.
Access control administration involves much more than unlocking a door. Someone must add and remove users, issue credentials, establish access permissions, create schedules, review events, manage doors, and respond when business requirements change.
Cloud-managed platforms are often designed around centralized administration through a supported browser or application interface. This can be useful when the people responsible for the system are not always located beside a dedicated security workstation.
For example, a property manager responsible for several commercial buildings may want an authorized administrator to manage users and supported system functions without maintaining a separate management process at every property. A growing company may also want administrators at headquarters to oversee access requirements for additional offices as they are added.
An on-premises platform can also provide sophisticated centralized administration. Enterprise systems may manage large numbers of doors, users, buildings, and locations. The distinction is therefore not that cloud systems can be centrally managed while on-premises systems cannot.
The more useful question is what infrastructure and administrative model each solution requires to provide that management.
An organization with an experienced internal IT department may be comfortable maintaining local system resources and may prefer the control that comes with doing so. Another business may not want responsibility for maintaining as much local management infrastructure and may find a cloud-managed architecture more practical.
Administrative experience also matters. A system that offers extensive capabilities but is unnecessarily difficult for the people who use it every day can create its own operational burden. The interface, permissions structure, reporting tools, credential workflow, and administrator roles should therefore be evaluated alongside the underlying architecture.
The goal is not simply to choose where the software resides. It is to choose a management approach that fits the people responsible for operating the system.
Difference 2: Remote Access and Multi-Location Management
Remote administration becomes increasingly important when an organization operates more than one facility or when the people responsible for access control regularly work away from the property.
This is one area where cloud-managed access control can be particularly attractive.
Many cloud platforms are designed to allow appropriately authorized administrators to manage supported functions across connected locations through a centralized interface. Instead of treating each facility as an isolated system, the organization may be able to manage multiple sites within a common administrative environment.
That can become valuable as a business grows. A company that begins with one Atlanta office may later add a warehouse, branch office, service facility, or another location in a different market. Centralized administration can make it easier to maintain consistent user-management processes as the organization expands.
Remote capability should still be evaluated platform by platform. The fact that a system is described as cloud-based does not mean every function can be performed remotely, nor does it mean every user should receive remote administrative authority.
On-premises systems can also support remote and multi-site management. Depending on the platform and network architecture, organizations may operate sophisticated systems across multiple buildings or geographically separated facilities while retaining locally hosted management infrastructure.
The difference can be the amount of infrastructure and IT planning required to accomplish that goal.
For organizations with established networks, internal IT expertise, and defined remote-access policies, that infrastructure may be completely appropriate. For organizations trying to expand without adding the same local management resources at every new facility, a cloud platform may offer a more convenient path.
That makes anticipated growth an important part of the decision. A business choosing an access control system only for today’s building may unintentionally create limitations when tomorrow’s second, fifth, or twentieth location arrives.
At the same time, growth alone does not automatically require cloud access control. Large on-premises platforms can scale extensively. The question is whether the organization’s preferred management model, IT resources, and system architecture can scale with the business in a practical way.
Difference 3: Capital Investment vs Recurring Subscription Costs
The financial structure of an access control system can influence the decision just as much as its technical capabilities.
Cloud-managed access control commonly involves some form of recurring software, licensing, hosting, or subscription expense. The exact pricing model varies by manufacturer and platform, so organizations should understand what is included, how fees are calculated, and how those costs may change as additional doors, users, features, or locations are added.
An on-premises system may place more of the investment into equipment, software, servers, installation, and other infrastructure purchased as part of the project. That does not mean an on-premises system has no continuing costs. Software support, maintenance agreements, upgrades, IT resources, replacement hardware, cybersecurity work, and service can all contribute to long-term ownership costs.
The distinction becomes important because organizations do not all budget in the same way.
A private business may be comfortable with predictable recurring expenses if those costs support capabilities it values, such as centralized management, easier multi-location administration, or a platform that can expand with the company. Another organization may prefer to make a larger capital investment and reduce its dependence on continuing subscription expenses.
Public-sector budgeting provides a useful example. A municipality may have capital funding available to purchase an access control system during the current budget year but may not be able to guarantee that recurring subscription expenses will receive funding in future annual budgets. In that circumstance, an on-premises architecture may be the more practical financial fit even when a cloud-managed platform offers capabilities the organization finds attractive.
The opposite can also occur. A growing company may prefer a recurring operating expense if it reduces the need to purchase and maintain some local management infrastructure and provides a practical way to expand administration as additional locations are opened.
This is why comparing only the initial proposal price can be misleading. Organizations should consider the expected cost structure over the useful planning horizon of the system, including applicable subscriptions, licensing, local infrastructure, maintenance, support, expansion, and internal IT requirements.
The objective is not necessarily to identify the architecture with the lowest first-year cost. It is to select a financial model the organization can realistically support throughout the period it expects to depend on the system.
Difference 4: IT Infrastructure, Updates and Maintenance
Access control increasingly overlaps with an organization’s information technology environment. That makes IT involvement an important part of comparing cloud and on-premises architectures.
An on-premises system may require the organization to maintain more of the local resources associated with system management. Depending on the platform, those responsibilities can involve servers or workstations, operating systems, databases, backups, network configuration, software updates, and coordination between security personnel and internal IT staff.
For an organization with an established IT department, that may not be a disadvantage. The company may already have standards for managing servers, networks, backups, user accounts, remote access, and system maintenance. Keeping more of the infrastructure within that environment may align well with existing practices.
For a smaller organization without those resources, the same responsibilities can become an operational burden.
Cloud-managed platforms can shift portions of the application infrastructure and service management away from equipment maintained directly by the customer. However, that should not be interpreted to mean that a cloud access control system eliminates the customer’s IT responsibilities.
The facility still requires appropriate network connectivity, and the organization may still need to manage administrator accounts, permissions, connected devices, network policies, identity practices, and other elements under its control. The exact division of responsibilities depends on the platform and service arrangement.
Software updates are another area where assumptions should be avoided. Some cloud services can deliver platform updates centrally, while an on-premises environment may require the organization or its service provider to plan and perform software upgrades locally. Actual update processes, support policies, maintenance requirements, and customer responsibilities vary by manufacturer.
Before choosing either architecture, the organization should determine who will be responsible for maintaining each major part of the system and whether those responsibilities match its internal resources.
A technically capable system can still become difficult to own if the organization does not have the people, processes, or support relationships required to maintain it properly.
Difference 5: Cybersecurity Responsibilities
Cybersecurity is sometimes reduced to an overly simple question: Is cloud or on-premises access control more secure?
That question does not have a universal answer.
Security depends on the architecture, manufacturer, configuration, credentials, network environment, administrative practices, software maintenance, authentication methods, and the responsibilities of the organizations involved.
A cloud-managed system places certain resources within a cloud-service environment, while the customer continues to control other portions of the deployment. An on-premises system gives the organization more direct responsibility for locally maintained infrastructure, but local ownership by itself does not guarantee stronger cybersecurity.
Organizations should instead evaluate how security responsibilities are divided and whether each party is prepared to manage the responsibilities assigned to it.
Administrator accounts deserve particular attention. Access to a security-management platform should be limited to authorized personnel, and available authentication and account-security features should be evaluated when selecting a system. Permissions should also reflect job responsibilities rather than giving every administrator unrestricted control.
Network design, software maintenance, credential practices, remote connectivity, backups, logging, and incident-response procedures may also be relevant depending on the platform and organization.
The cybersecurity discussion should therefore involve both the security integrator and the customer’s IT personnel when appropriate. The objective is to understand how the proposed access control architecture fits within the organization’s broader cybersecurity requirements rather than assuming that choosing either “cloud” or “on-premises” settles the issue.
Difference 6: Scalability and Expansion
Growth is one of the strongest reasons to evaluate system architecture before selecting an access control platform.
A business may begin with a single building and a relatively small number of controlled doors. Over time, it may add employees, departments, entrances, warehouses, gates, branch offices, or facilities in other cities. The access control system should be evaluated not only for what the organization needs today but also for the growth it can reasonably anticipate.
Cloud architecture can be attractive in this situation because cloud computing is designed around concepts that include broad network access and the ability to provision resources as demand changes. The National Institute of Standards and Technology’s definition of cloud computing identifies characteristics including broad network access, rapid elasticity, and measured service. Those characteristics help explain why cloud architecture can support flexible growth, although the actual scalability of an access control system still depends on the specific product and manufacturer.
For an expanding business, a cloud-managed access control platform may make it easier to bring additional supported locations into a common management environment without recreating the same management infrastructure independently at every facility.
That can be particularly useful when growth is geographic. Administrators may want consistent credential policies, user-management practices, reporting, and oversight across several locations rather than operating each site as a separate security environment.
However, cloud should not be treated as a synonym for unlimited scalability.
Every access control platform has design parameters, licensing structures, supported hardware, network requirements, and other practical limitations that should be evaluated before purchase.
Likewise, it would be inaccurate to characterize on-premises systems as suitable only for smaller organizations. Enterprise on-premises platforms can support substantial numbers of users, doors, buildings, and geographically dispersed facilities.
The meaningful difference is often how expansion is accomplished and what additional infrastructure, licensing, administration, and IT resources are required as the system grows.
A company expecting significant expansion should therefore ask an integrator to demonstrate how each proposed architecture would accommodate the organization’s realistic growth plan—not simply whether the product can support another door.
Difference 7: Long-Term Operational and Financial Fit
The final comparison brings the previous six differences together. An access control system should fit not only the facility where it is installed but also the organization responsible for operating and funding it over time.
A system can be technically capable and still be the wrong choice if its management requirements, cost structure, IT responsibilities, or expansion model do not fit the organization.
This is why long-term planning should include more than the number of doors being controlled today. Decision-makers should consider how the organization expects to change, who will administer the system, what internal resources will be available, how future expenditures are approved, and whether additional locations are likely.
For some organizations, the predictability of owning and maintaining more of the system infrastructure locally may be important. For others, the ability to use a cloud-managed platform without building the same management infrastructure at each new location may be more valuable.
The expected life of the system also matters. Organizations should understand applicable software licensing, subscription requirements, manufacturer support policies, upgrade paths, hardware availability, and other continuing costs before committing to either architecture.
A lower initial cost does not necessarily produce the lowest long-term cost, and a higher initial investment does not necessarily create the better long-term value. The useful comparison is the total operational and financial fit of the proposed system over the period the organization expects to use it.
When On-Premises Access Control May Be the Better Fit
On-premises access control can be the better choice when an organization has a strong reason to maintain more direct control over its local system infrastructure and has the resources required to support that approach.
An organization with an established IT department may already have the servers, network architecture, backup procedures, cybersecurity policies, and personnel necessary to manage locally hosted applications. In that environment, adding an on-premises access control platform may align naturally with existing technology practices.
Financial structure can be another deciding factor.
Organizations that prefer capital expenditures over continuing subscription costs may find an on-premises model attractive. This can become particularly important for public agencies, institutions, or other organizations operating under annual budget approvals.
Consider the municipal example discussed earlier. A city may have approved capital funding available this year to purchase and install an access control system. That does not necessarily mean administrators can guarantee that a future governing body or annual budget will approve recurring subscription expenses every year for the life of the system.
In that situation, selecting an appropriate on-premises platform can be a sound operational decision. The organization is not rejecting cloud technology. It is selecting an architecture that better matches the way its technology expenditures are funded.
On-premises may also make sense when organizational policies require certain system resources to remain within infrastructure controlled directly by the organization, provided the selected platform can meet the operational and security requirements of the project.
None of these conditions means an on-premises system requires no continuing investment. Hardware maintenance, software support, upgrades, backups, cybersecurity, IT labor, and eventual equipment replacement should still be included in the ownership plan.
When Cloud Access Control May Be the Better Fit
Cloud-managed access control can become particularly attractive when an organization expects growth, operates multiple locations, or wants authorized administrators to manage supported system functions without depending on the same local management infrastructure at every facility.
Consider a company with one Atlanta location that expects to open additional offices or facilities over the next several years. If the selected cloud platform is designed for centralized multi-site administration, new locations may be brought into a common management environment as the organization expands.
That can simplify more than adding doors. It may help an organization maintain consistent administrative practices across locations, manage users centrally, and give appropriately authorized personnel visibility into supported functions without treating every facility as a completely separate management environment.
Cloud can also be useful for organizations that do not want to maintain as much locally hosted application infrastructure themselves. Depending on the platform and service model, portions of software hosting, platform maintenance, and updating may be handled as part of the cloud service.
That convenience does not eliminate the customer’s responsibilities. Local access control equipment still requires proper installation and service. Network connectivity remains important, administrator accounts must be protected, and the organization still needs policies governing who can manage the system.
The principle of limiting administrative authority is relevant regardless of architecture. The National Institute of Standards and Technology describes the principle of least privilege as providing only the access and authorizations needed to perform assigned functions. Applying that principle to system administration can help organizations think carefully about who actually requires access to security-management functions.
A cloud platform therefore should not be selected merely because it is cloud-based. It becomes the better choice when its management model, capabilities, recurring cost structure, cybersecurity approach, and expansion path align with the organization’s requirements.
Questions to Ask Before Choosing an Architecture
The strongest access control decisions usually begin with operational questions rather than product names.
How many locations need to be managed today, and how many might exist several years from now? Who will administer the system? Will administrators regularly work away from the facility? Does the organization have internal IT personnel capable of maintaining local system infrastructure? Are recurring subscriptions acceptable within the organization’s budgeting model?
Security requirements should be considered as well. The organization should understand how administrator accounts are protected, how permissions are assigned, what network connectivity is required, who is responsible for software maintenance, and how responsibilities are divided among the customer, integrator, manufacturer, and cloud provider where applicable.
Growth deserves its own discussion. Adding several doors to an existing building is different from adding ten geographically separated facilities. The proposed system should be evaluated against the organization’s realistic expansion plans rather than an undefined promise that it is “scalable.”
Organizations should also consider how access control fits with other security requirements. Video surveillance, gated entry, visitor management, alarms, and other systems may affect platform selection when integration or coordinated operation is part of the project.
Atlanta Access Controls provides commercial access control and integrated security services for organizations evaluating new systems, existing infrastructure, expansion, and modernization. Looking at the complete security environment can help identify requirements that may not be obvious when access control is considered by itself.
These questions do not automatically point toward cloud or on-premises architecture. They provide the information needed to determine which architecture better fits the organization.
Planning Your Access Control System With Atlanta Access Controls
The choice between cloud and on-premises access control should ultimately support the way an organization operates.
A municipality concerned about guaranteeing future subscription funding may have a strong reason to select an on-premises platform. A growing company expecting additional locations may place greater value on the centralized administration and expansion model offered by an appropriate cloud-managed system. An organization with substantial internal IT resources may prefer more direct responsibility for local infrastructure, while another may deliberately choose to reduce that responsibility.
Those are legitimate differences, and they are why the answer should come from an assessment of the organization rather than a predetermined preference for one technology.
Atlanta Access Controls can evaluate the number and types of controlled openings, existing infrastructure, administrative requirements, IT environment, anticipated growth, related security systems, and financial considerations before recommending an architecture.
The objective is not to sell a business “cloud” or “on-premises.” It is to design an access control system that the organization can realistically operate, support, expand, and fund.
Contact Atlanta Access Controls to discuss your commercial access control project and evaluate which system architecture better fits your facility, organization, and long-term plans.